Adversarial exposure validation
Prove what an attacker can actually reach
You set an objective and goal-driven agents reason about what they find, chain techniques dynamically, and adapt to the security controls in their path. Every action is mapped to MITRE ATT&CK and correlated against the Sigma, Splunk and Elastic rules you already run.

Cyber range platform
Simulation Range
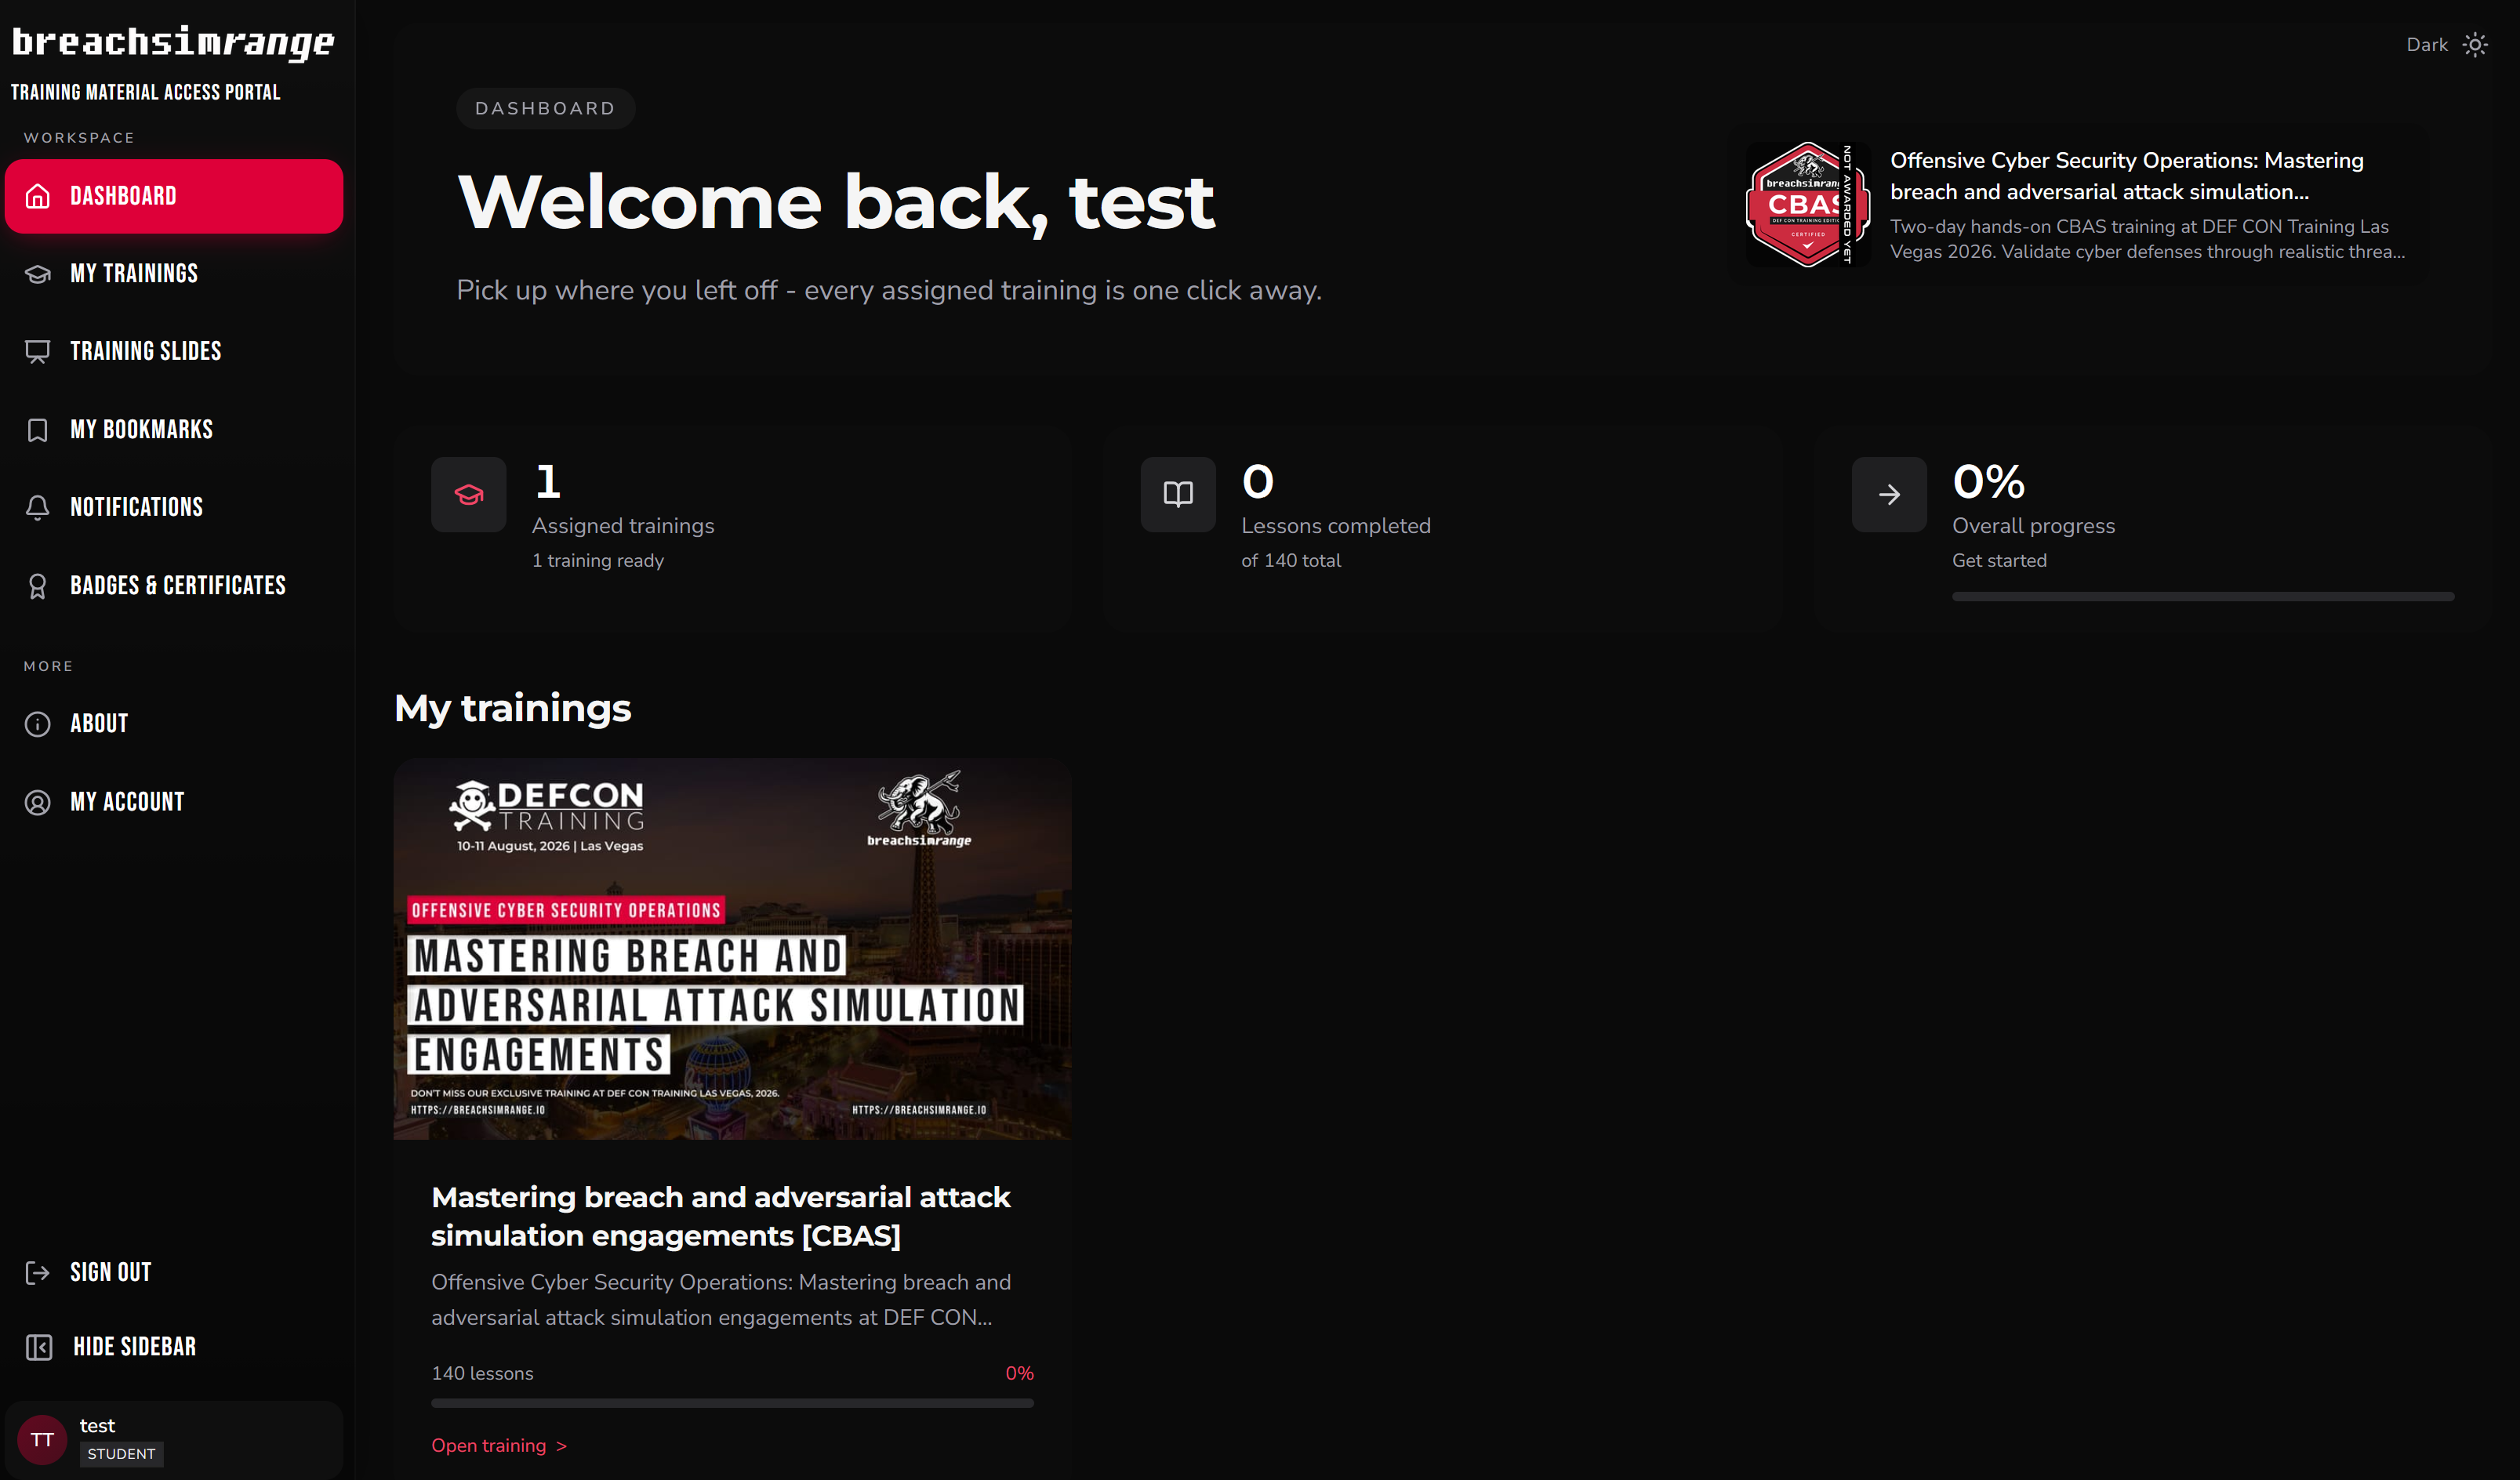
The cyber ranges and the training management system run on one platform, on infrastructure we build and operate ourselves rather than a third-party lab provider. Teams work through the material, then attack a live enterprise environment that has EDR, antivirus, web proxies and SIEM in it.
It is the same platform we run our DEF CON trainings and the CBAS certification on.
Incident response platform
Incident Range
Incident Range is for responding to, containing and managing incidents in an organization. It integrates with the log sources and platforms you already run, either over APIs or by uploading raw logs, and keeps the investigation and the incident record in the same place.
