Emulate the adversary. Simulate the breach. Prove your defenses.
One platform for breach and adversary simulation: emulate the threat actors, ransomware and techniques targeting you, build and execute dynamic agent-driven campaigns, and run AI-assisted adversary attack simulation exercises, all validated against MITRE ATT&CK.
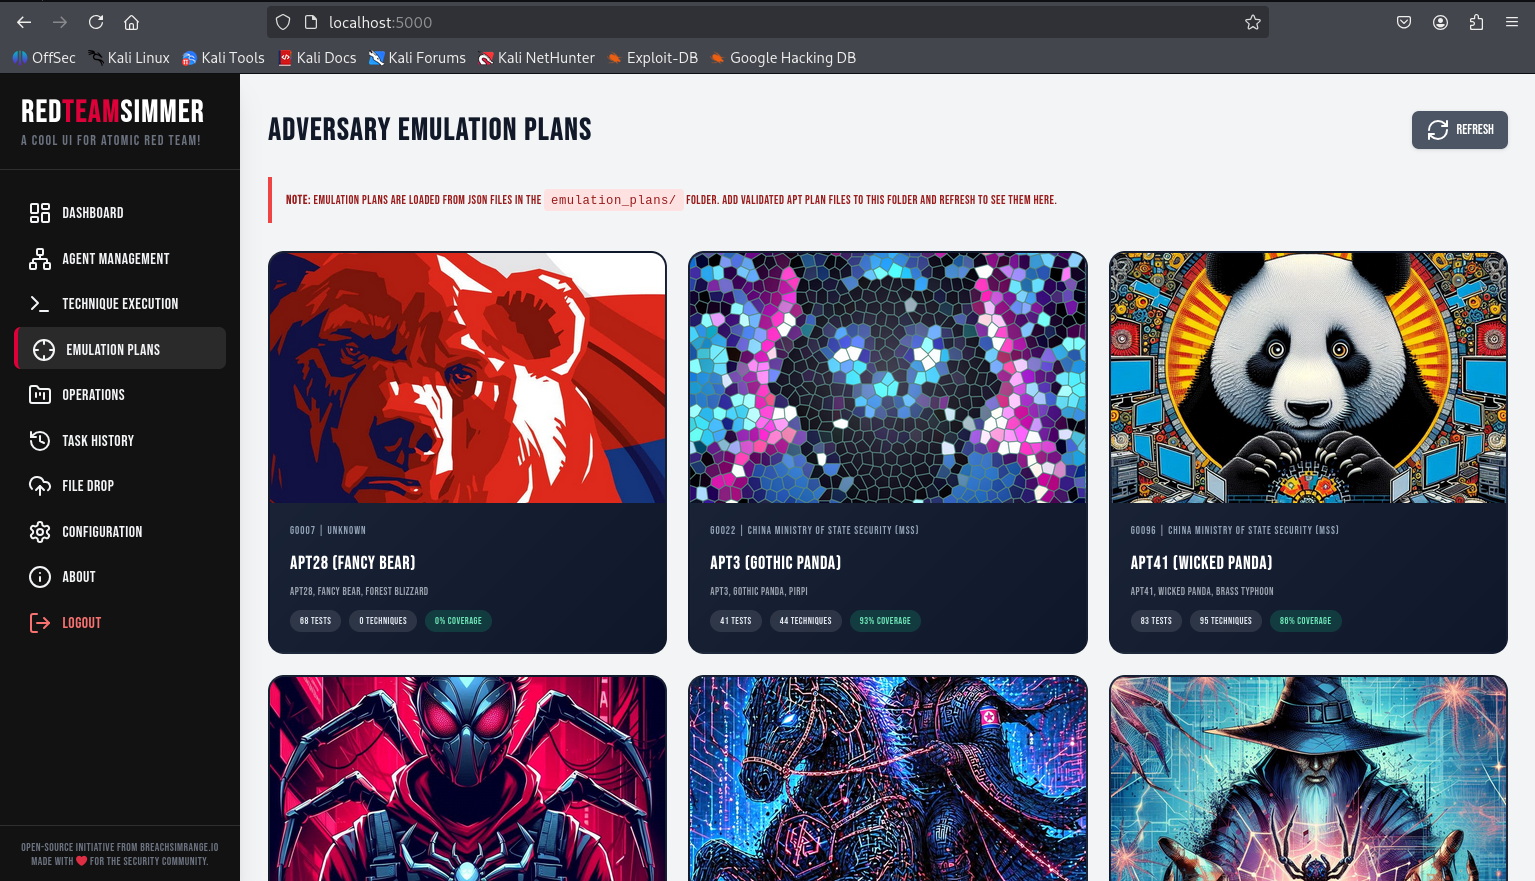
Adversary emulation
Run the known threat actors, ransomware and atomic techniques targeting you, mapped to MITRE ATT&CK.
Dynamic adversary simulation
Build and execute goal-driven campaigns an agent runs on its own, from a single foothold to full compromise.
AI-assisted attack simulation
Turn raw threat intel into ready-to-run exercises, with AI that generates and adapts payloads, plans and campaigns.
What is RedTeamSimmer?
RedTeamSimmer is an AI-assisted breach and adversary simulation platform. Instead of following a fixed script, you set an objective and goal-driven agents reason about what they find, chain techniques dynamically, and adapt to the security controls in their path, all within guardrails and with a human in the loop.
What does it do?
It deploys a lightweight agent as an ordinary user and lets it operate like a real adversary: enumerating your environment, harvesting and abusing credentials, moving laterally and escalating toward your most critical assets. Every action is mapped to MITRE ATT&CK and you see exactly what your defenses catch.
The AI arms race
Your adversaries already use AI. So should testing your defenses.
Attackers use generative AI to build tooling, write lures and reshape malware on the fly. Waiting to see how they hit you is not a strategy. RedTeamSimmer Enterprise puts that same capability on your side, using AI to emulate and simulate real attacks against your own environment, continuously and proactively, so you find and fix what they would exploit before they ever get the chance.
Know your defenses before an adversary does
Prove your defenses work. Continuously.
A pentest is a snapshot. Your environment, your detections and the threat landscape change every week. RedTeamSimmer Enterprise runs safe, real-world attacks against your production-grade environment on demand and on a schedule, so you always know what you detect, what you miss, and exactly what to fix next.
MITRE ATT&CK v19 tactics covered end to end, from Initial Access to Impact.
AV and EDR products fingerprinted by the agent, including CrowdStrike, SentinelOne and Defender.
Detection sources correlated per technique: Sigma, Splunk and Elastic rules.
Lightweight Go agent, no dependencies, ready for on-prem, cloud or air-gapped estates.
One platform, two engines
Known techniques and the full, dynamic breach
RedTeamSimmer Enterprise combines classic breach and attack simulation with dynamic, agent-driven adversary simulation, so you validate the techniques you expect and uncover the attack paths you have not.
Validate the techniques you already know
Run curated threat-actor plans, ransomware scenarios and atomic techniques on demand and on a schedule. Every result is correlated to your detections and scored against MITRE ATT&CK, so you can prove prevention and detection coverage technique by technique.
Continuous control validation, detection engineering and purple-team exercises against a defined, repeatable technique set.
Deploy an agent and trace the full attack path
Give an agent a starting point and it builds and executes an advanced simulation on its own, reasoning about the environment, chaining techniques and propagating as far as your controls allow, all inside strict guardrails.
Drop the agent in as a standard domain user and it dynamically simulates the whole breach: enumerating the forest, abusing credentials and delegation, moving laterally and showing exactly how far it can propagate toward domain dominance.
Adversary emulation
Launch a real threat actor in a few clicks
Choose a group, a ransomware scenario or a custom kill chain and run it across your estate. No scripting to memorize, automatic prerequisite handling, and live, color-coded results streaming into one console.
- Multi-stage plans modeled on real tradecraft
- Atomic technique testing at fleet scale
- Safe, controlled, fully reversible execution
Coverage and gaps
See your posture on the ATT&CK matrix
Every technique you run is correlated against Sigma, Splunk and Elastic detection logic and rendered as a live MITRE ATT&CK heat map. Track prevention and detection coverage technique by technique, and watch it climb as you tune.
- Detected, missed and prevented, side by side
- Detection rule mappings out of the box
- Coverage trends over time and Navigator layer export
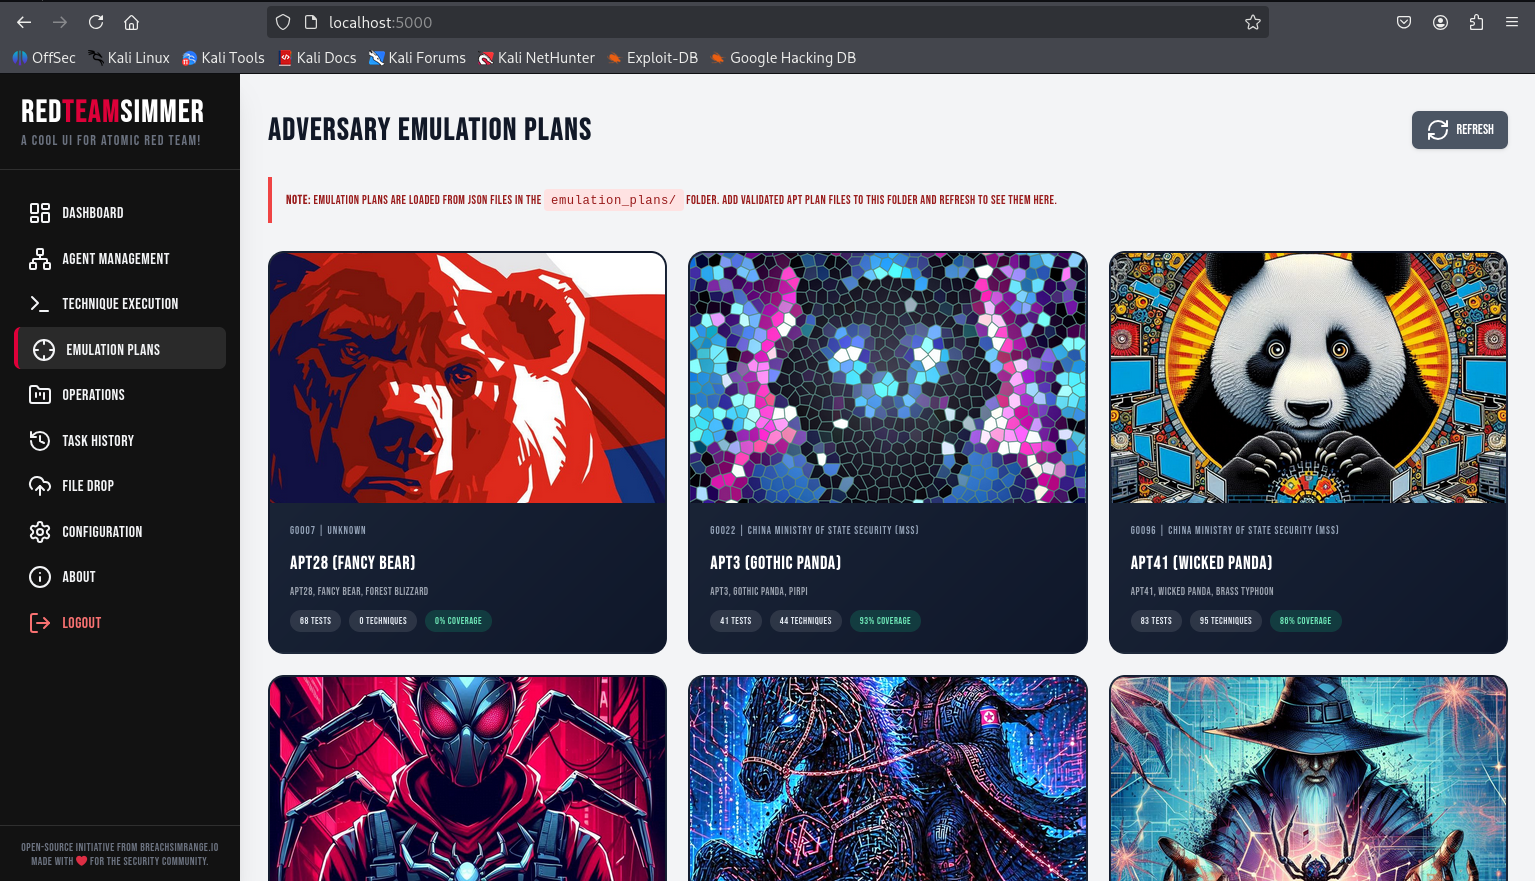
Deep technical simulation plans
Test the tradecraft that actually breaks defenses
Go far beyond checkbox testing. RedTeamSimmer Enterprise ships purpose-built plans for the techniques modern adversaries really use.
Automated Active Directory Breach
One click maps and attacks your AD: enumeration, Kerberoasting, AS-REP roasting, DCSync, delegation and ACL abuse and lateral movement, charting the real routes from a single foothold to domain dominance.
EDR Evasion Techniques
Exercise AMSI and ETW tampering, user-mode unhooking, indirect syscalls, sleep obfuscation and in-memory execution to see what your endpoint stack truly catches.
Web Proxy and Egress Bypass
Validate exfiltration and C2 over HTTP(S) proxies, DNS and domain fronting to confirm your egress filtering, TLS inspection and DLP hold under pressure.
Cloud Attack Simulation
Emulate identity abuse, misconfiguration exploitation, privilege escalation and persistence across AWS, Azure and GCP, mapped to ATT&CK for Cloud.
Supply Chain Attack Simulation
Rehearse poisoned dependencies, compromised build pipelines and trusted-update abuse to test how far an upstream compromise could spread inside your org.
AI Attack Simulation
Probe your own AI systems: prompt injection, jailbreaks, model and data poisoning, and the abuse of AI agents and integrations across the attack surface.
Threat Intel URL to Plan
Paste a threat intel report URL or raw intelligence and the AI classifies it, extracts the TTPs, maps them to MITRE ATT&CK and assembles a ready-to-run adversary emulation plan for the threats that target you.
Ransomware Kill Chain
Safely simulate ransomware end to end: initial access, lateral movement, encryption behavior and impact, to validate prevention, detection and response.
Defense Evasion and Obfuscation
Layer in payload mutation, living-off-the-land binaries and obfuscation so you test detection resilience, not just static signatures.
Ransomware readiness
Test your defenses against ransomware, safely
Ransomware is the impact scenario boards ask about most. RedTeamSimmer Enterprise lets you rehearse it end to end, both the strains already hitting your sector and the mutations you have never seen, without ever putting real data at risk.
Emulate real ransomware strains
Run faithful, safe emulations of the families operating today, from initial access through lateral movement, encryption behavior and impact, each mapped to MITRE ATT&CK so you can prove what your prevention, detection and response actually catch.
Simulate custom ransomware with AI
Have AI generate and mutate a bespoke ransomware campaign on demand, with novel tooling and behavior, to stress-test detection resilience against threats that do not exist in any signature database yet.
Dynamic adversary simulation: Active Directory
From a standard user to domain dominance
The clearest example of dynamic simulation. Deploy the agent as an ordinary domain user and it decides its own path, enumerating the forest, abusing credentials, Kerberoasting, DCSync, delegation and ACLs, and moving laterally to show exactly how far a single compromised account can propagate through your infrastructure.
The thing driving this is not a chatty, on-host AI agent. It is a compiled Go agent with built-in tool calling that stays in continuous contact with the RedTeamSimmer SaaS platform, exactly like a red team operating through a command-and-control channel.
A real Go agent, not an LLM loop
A lean, compiled Go beacon with a fixed tool set runs on the host. No local model and no blind command spraying, so the footprint on the endpoint stays minimal.
The platform AI does the thinking
The beacon streams telemetry back to the SaaS platform. The platform AI analyzes what is happening in the environment and returns the next command and MITRE technique to execute.
Beacons spread with the breach
As it compromises new hosts, the agent deploys fresh beacons and keeps them under one operator view, propagating from the initial foothold toward the target the way a human red team would.
Signal, not noise
Because the reasoning happens on the platform and only vetted commands reach the host, you avoid the heavy, noisy, unnecessary execution a naive on-host AI agent generates. Every action is deliberate.
Ready to see your AD security in focus?
Get a custom assessment showing all attack paths in your forest and the exact mitigations needed.
Secure by design
Guardrails on every action
Running offensive techniques against production demands absolute trust. Every action executes inside policy-defined guardrails, and a safety layer validates that each step is in scope, proportionate and reversible before it ever runs.
Pre-flight check
Each action is assessed for scope and impact before execution.
Scoped blast radius
Targets, techniques and timing bounded by policy.
Reversible by default
Non-destructive actions with clean rollback and artifact cleanup.
Instant kill switch
Approval workflows and one-click stop, fully audited.
Integrations
Native SIEM integration, built in
Every executed technique is correlated to your detection content and pushed into the SIEM your SOC already runs, so simulation results and the alerts they fire land side by side.
Splunk integration
Ships ready-to-use SPL queries per technique and forwards simulation events into Splunk, so you can confirm which runs generated alerts and tune SPL detections against real attacker behavior.
Elastic SIEM integration
Maps each technique to Elastic Security detection rules and streams results into Elastic, closing the loop between what you simulated and what your Elastic SIEM caught.
Beyond SIEM, results map cleanly onto the detection content, endpoint tooling, platforms and clouds your teams already operate.
Deployment & architecture
One binary. Any environment.
A single compiled agent registers with your server, reports host details and streams results in real time. Built to run wherever your estate runs, including restricted and offline networks that cloud tools cannot reach.
Standalone Go agent
Compiled binary with no external dependencies. Configurable poll intervals and jitter for realistic, low-noise operations.
On-prem, cloud or air-gapped
A local, offline rule database means no external API calls fire during a run, making it suitable for restricted and segmented networks.
Central console
One view of active agents, coverage, task history and failed-operation triage, with paused, resumed or stopped operations under your control.
Clean removal
Staged technique files and agent artifacts are removed on completion or clean shutdown, with nothing left behind.
How it works
From deploy to defended in four steps
Deploy
Roll out lightweight agents across your estate, on-prem, cloud or air-gapped, in minutes.
Plan
Pick a threat actor, a ransomware scenario or a technical plan, or set an objective and let the agent decide.
Execute
Run safe, guardrailed techniques and watch live, color-coded results stream into a single console.
Measure
Get ATT&CK coverage, detection gaps and prioritized fixes, then re-run to prove the fix worked.
Who it's for
Built for offense, defense and the boardroom
An AI-assisted breach and attack simulation platform your whole security organization can pick up and run. Offensive teams, defenders and CISOs each get hands-on results they can act on.
Scale coverage without losing depth
Let AI-driven agents run full campaigns and atomic testing at fleet scale, freeing operators for the tradecraft that still needs a human.
Emulate any threat actor on demand
Spin up the groups, ransomware and TTPs targeting you, then let AI turn fresh threat intel into a runnable campaign in minutes.
Validate and tune detections
Fire techniques on demand, see exactly which Sigma, Splunk or Elastic rules light up, and close the gaps that matter before an adversary finds them.
Exercise the response
Rehearse real intrusion behavior end to end so analysts train against genuine adversary tradecraft, not tabletop hypotheticals.
Measure real risk reduction
Board-ready MITRE ATT&CK coverage and trend metrics that show defenses improving over time, not a once-a-year snapshot.
Prove control effectiveness
Continuous, repeatable validation with per-technique evidence to back your control assertions for audits and the board.
Why regulators require it
Breach simulation is becoming a mandate, not an option
Across the UAE, India, the US and the EU, financial regulators and national cyber authorities now require banks and critical organizations to run offensive, intelligence-led testing of their defenses. Continuous breach and attack simulation is how you meet that bar and prove it.
The Central Bank of the UAE (CBUAE) and the UAE Cyber Security Council require licensed financial institutions to build cyber and operational resilience and to validate controls through offensive security testing, in line with the National Information Assurance (NIA) standards.
CBUAE regulationsThe Reserve Bank of India (RBI) Cyber Security Framework mandates that banks run regular vulnerability assessment, penetration testing and, for larger banks, red-team exercises, with CERT-In setting national incident and testing expectations.
RBI Cyber Security FrameworkThe FFIEC (Federal Financial Institutions Examination Council) expects institutions to conduct penetration testing and threat-led red-teaming, while CISA promotes continuous validation of security controls against real adversary behavior.
FFIEC guidanceUnder DORA (Digital Operational Resilience Act), financial entities must undergo Threat-Led Penetration Testing (TLPT), following the TIBER-EU framework from the European Central Bank, essentially intelligence-led breach and attack simulation.
ECB TIBER-EUReferences point to the official regulators and frameworks. Requirements vary by institution size and license; check the current text for your obligations.
Threat-actor and ransomware library
Emulate the groups actually targeting you
A curated, continually updated library of adversary emulation plans built from real-world tradecraft and mapped to MITRE ATT&CK. All accessible in the early access program.
APT28
Nation-state, spear-phishing, lateral movement.
APT41
Cyberespionage, supply chain, privilege escalation.
FIN7
Financial targeting, credential theft, ransomware.
Lazarus Group
State-sponsored, destructive malware, custom implants.
Wizard Spider
Ransomware ops, Trickbot C2, extortion.
APT3
Gothic Panda, browser exploits, credential access.

The Philosophy.
A tusker with a spear
Our mark is a tusker carrying a spear. It is exactly how we think about offensive security.
- The tusker is patient, powerful and never forgets a threat, the resilience your defenses are built to have.
- The spear is the offensive edge: precise, deliberate, and aimed at what actually matters.
- Together they are our philosophy: think like the adversary, strike with precision, and leave your defenses stronger than you found them.
Offensive mindset. Defensive impact.
Built by practitioners
From working offensive security operators
RedTeamSimmer Enterprise is built on RedTeamSimmer, the open-source adversary emulation and Atomic Red Team orchestration platform from the BreachSimRange team, presented to the security community at DEF CON Demo Labs Singapore and Black Hat USA Arsenal 2026. When new tradecraft appears, our specialists reverse it, weaponize it safely and ship it as a ready-to-run plan.
Fast turnaround
Emerging TTPs reversed and shipped as ready-to-run plans.
Community proven
Open-source roots, shown at DEF CON and Black Hat Arsenal.
ATT&CK aligned
Every technique mapped to MITRE ATT&CK v19 out of the box.
Validated before ship
Each plan is reviewed and tested before it reaches your console.
Editions
Built for consultants and enterprises
RedTeamSimmer Enterprise ships in two editions on one platform. The Consultants edition is tuned for delivering engagements to clients; the Enterprise edition adds the features an in-house team needs to run continuous validation as a program.
Deliver sharper engagements
For pentest and red-team consultancies. Deploy quickly at a client, run adversary emulation and deep technical plans, and hand over clear, ATT&CK-mapped findings, engagement after engagement.
Run validation as a program
For in-house security teams. Everything in the Consultants edition, plus continuous scheduling, native SIEM integration, coverage trending and enterprise access controls to operate at scale over time.
Under active development
Join the Early Access Program
Be among the first organizations to experience next-generation adversary emulation. RedTeamSimmer Enterprise is currently in active development. We are opening limited early access slots to organizations that want to:
Try the Next Generation
Experience agentic adversary emulation before general availability.
Get Priority Support
Direct access to the engineering team and priority support as we develop new capabilities.
Shape Development
Influence roadmap decisions and feature development based on your feedback.
Only accepting select organizations. Request early access now to get on the list.
Questions, answered
Frequently asked questions
What is breach and attack simulation (BAS)?
Breach and attack simulation is the practice of safely running real attacker techniques against your own environment, on demand and continuously, to see which ones your controls actually prevent and detect. Instead of waiting for a real incident or an annual pentest, BAS turns known adversary behavior into repeatable tests and measures the results against a framework like MITRE ATT&CK, so you always have current evidence of where your defenses hold and where they do not.
How can RedTeamSimmer Enterprise be used?
Deploy the lightweight agent across your estate, then run it two ways: as a BAS platform, firing curated threat-actor plans, ransomware scenarios and atomic techniques to validate detections; and as a dynamic adversary simulator, where you set an objective and an agent builds and executes the attack on its own, such as breaching Active Directory from a standard user. Detection engineers use it to tune rules, SOC and purple teams to exercise response, red teams to scale coverage, and leadership to track measurable risk reduction over time.
Is it safe to run against production?
Yes. Every action runs inside policy-defined guardrails and is checked for scope and impact before it executes. Techniques are non-destructive and reversible by default, blast radius is bounded by policy, and an instant kill switch stops any run. Staged files and agent artifacts are cleaned up automatically on completion.
How is this different from a penetration test?
A pentest is a point-in-time snapshot. RedTeamSimmer Enterprise runs continuously and on a schedule, so you measure your detection and prevention posture as your environment and the threat landscape change, and re-run instantly to prove a fix worked.
Which detection tools does it work with?
Each executed technique is correlated against Sigma, Splunk and Elastic detection content, with per-technique rule counts and links to the upstream sources. Coverage is rendered on a live MITRE ATT&CK heat map and can be exported as an ATT&CK Navigator layer.
Can it run in an air-gapped or restricted network?
Mostly, yes. The agent is a standalone Go binary and the detection rule database is local and offline, so the emulation features run fully air-gapped: adversary emulation plans, atomic techniques and detection correlation all work with no external calls. The AI-enabled features are the exception. Agentic, goal-driven dynamic simulation relies on the platform AI reached over the C2 channel, so it needs connectivity and will not work in a fully air-gapped network. In segmented or restricted estates you get the complete emulation capability offline, and the AI-driven simulation wherever the agent can reach the platform.
What does the agentic simulation actually do?
You set an objective instead of a fixed script. Goal-driven agents reason about what they find, select and chain techniques dynamically, and adapt to the controls in their path, all within guardrails, with a human in the loop and full replay of every decision.
How do we get access?
RedTeamSimmer Enterprise is in active development with limited early access for select organizations. Request access below and our team will follow up to scope a deployment and walk you through a live demo.