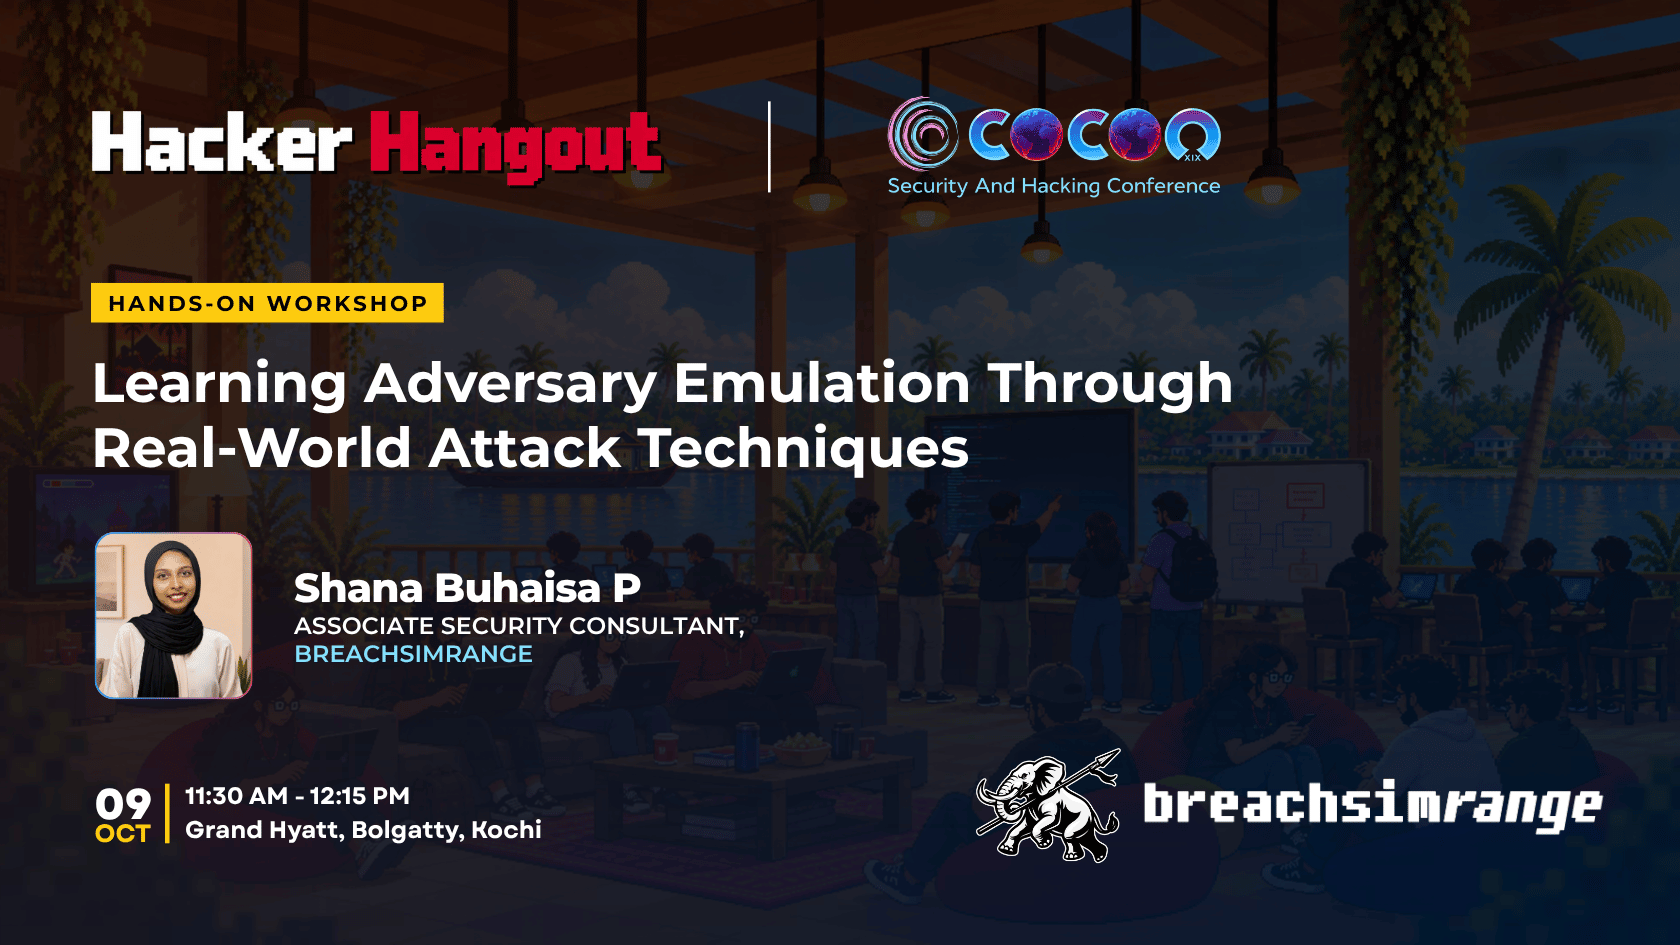
This hands-on workshop introduces security practitioners and enthusiasts to the foundations of adversary emulation. Participants learn how real-world threat actors execute attacks across different stages of an intrusion, how to map adversary techniques to the MITRE ATT&CK framework, and how to safely emulate these behaviors in controlled environments to evaluate defensive visibility and detection capabilities. c0c0n 2026 · Hacker Hangout
Shana Buhaisa P, Associate Security Consultant at BreachSimRange, delivered a hands-on workshop at Hacker Hangout village track supported by DEF CON Group Trivandrum in c0c0n 2026 on learning adversary emulation through real-world attack techniques. The session gave attendees a practical look at threat emulation, showing how real-world attackers operate. It broke down complex attack techniques into hands-on steps, helping participants understand how adversaries move through systems and how their tactics can be tested in realistic scenarios.
Throughout the workshop, Shana guided participants through practical exercises connecting cyber threat intelligence (CTI) with offensive execution. Attendees explored how real-world attack techniques are mapped to the MITRE ATT&CK framework, executed using emulation tools and scripts, and chained together across the attack lifecycle. The session also examined how defensive controls such as EDR and SIEM record these activities, giving participants visibility into both attacker tradecraft and detection opportunities.

BreachSimRange runs red teaming, threat-led breach and adversary simulation that mirror how modern threat actors operate, so you find the gaps before they do.
Talk to us about Consulting